Zero-Trust for a 40-Person Company: A Practical Rollout Playbook
Monty Adams
SR. CUSTOMER SECURITY ENGINEER
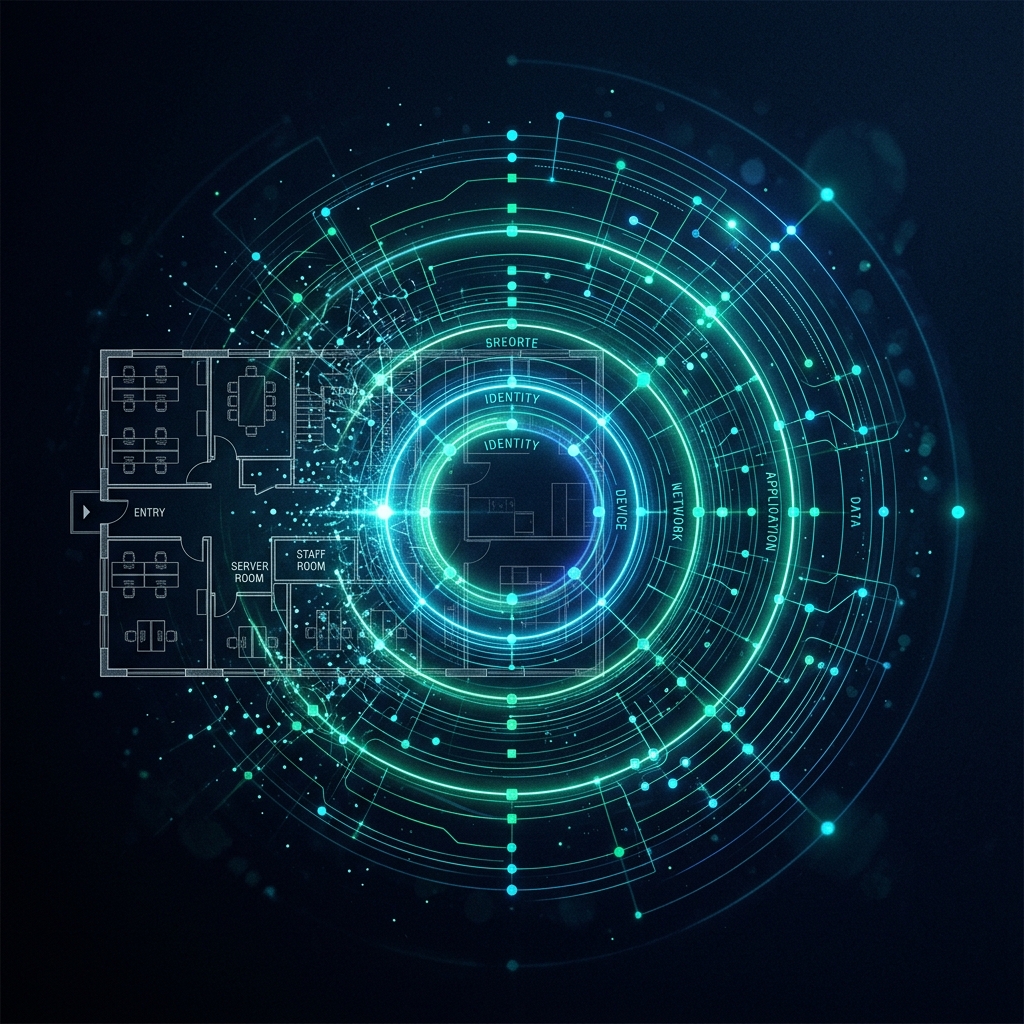
Zero-trust has a marketing problem: it sounds like something that demands a dedicated security team and a seven-figure budget. In practice, a 40-person company can reach a genuinely zero-trust posture in under a month with tools it mostly already owns. Here's the playbook we run.
Week 1 — Kill the flat network
Segment first. Guest Wi-Fi, staff devices, servers and printers should never share a broadcast domain. Modern firewalls make this a configuration exercise, not a forklift upgrade. Containment is the single highest-leverage control a small network can gain.
Week 2 — Identity becomes the perimeter
- Phishing-resistant MFA on every account — no exceptions for executives.
- Conditional access: unknown device plus unusual location equals challenge or deny.
- Retire the shared-office VPN in favor of identity-aware, per-app access (ZTNA).
- One identity provider as the source of truth — no orphan local accounts.
Week 3 — Devices prove themselves
Enroll every endpoint into management so only known, patched, encrypted devices can reach company data. Personal devices get a separate lane with access to email only — never file shares.
Week 4 — Watch what you built
Zero-trust without monitoring is just architecture. Stream authentication and network logs somewhere they're actually reviewed — a managed SOC is the realistic answer at this size — and rehearse the response runbook once. Then maintain: quarterly access reviews, because trust, once granted, silently accumulates.